Most business owners assume hackers target big companies. They don't. Automated bots don't check your revenue before they attack — they scan the entire internet for outdated plugins and weak passwords, and a small accounting firm is just as likely a target as anyone else.
We know this because we watch it happen every day.
The numbers
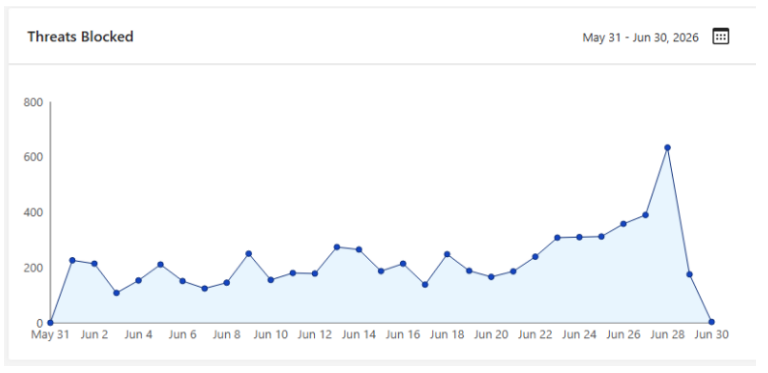
Over a 30-day period, our Web Application Firewall blocked 3,888 brute force attacks against a single client — a Queensland accounting firm with no reason to think of itself as a target. On the worst day, that number spiked to 680 attacks in 24 hours.
The client never knew any of it happened. That's the point.
[Chart: Threats Blocked, May 31 – Jun 30, 2026]
We saw a similar pattern with another client, an online training platform that experienced over 100 hacking attempts in a single month — every one blocked before it reached their live users.
Why this matters if you own a WordPress site
Every WordPress site is a target, regardless of size, industry, or how "boring" you think your business is to a hacker. Automated attacks don't discriminate — they're looking for the same handful of common weaknesses on every site they scan:
- Outdated plugins with known vulnerabilities
- Weak or reused admin passwords
- No firewall between the internet and your login page
- No monitoring to catch an intrusion before it causes damage
Most business owners only find out they've been compromised after it's already cost them — lost traffic, a Google blacklist warning, or a frantic call to whoever built their site originally.
What "blocked" actually looks like
A brute force attack is exactly what it sounds like: a bot repeatedly guessing usernames and passwords at your login page, thousands of times, until something works. A properly configured Web Application Firewall stops these before they ever reach WordPress itself — the attack fails at the edge, not at your login form.
That's the difference between a site that's protected and a site that's just hoping nothing bad happens.
The takeaway
If your website has been live for more than a few months, it has almost certainly already been targeted — you just don't have the logs to know it. The absence of a "we got hacked" story isn't proof you're safe. It might just mean nobody's shown you the attack data yet.
Source: IMD WAF logs, client accounts referenced with permission, identifying details withheld. Internet Marketing Direct has provided WordPress hosting, security, and maintenance to Australian businesses since 2009.
Is your website actually protected, or just hoping for the best?
and we'll show you what's really happening behind the scenes.